Customers can register accounts and thereby gain the ability to:
The activeCustomer query will return a Customer object if the customer is registered and logged in, otherwise it will return null. This can be used in the storefront header for example to
determine whether to display a "sign in" or "my account" link.
The login mutation is used to attempt to log in using email address and password.
Given correct credentials, a new authenticated session will begin for that customer.
The logout mutation will end an authenticated customer session.
The login mutation, as well as the following mutations related to registration & password recovery only
apply when using the built-in NativeAuthenticationStrategy.
If you are using alternative authentication strategies in your storefront, you would use the authenticate mutation as covered in the External Authentication guide.
The registerCustomerAccount mutation is used to register a new customer account.
There are four possible registration flows.
If authOptions.requireVerification is set to true (the default):
If authOptions.requireVerification is set to false:
Whatever the setting, if an account already exists for that email address through another authentication strategy (for example an SSO provider) and has no password yet:
{ success: true } exactly as it does for a new account, so it does not reveal
that the account exists. The password is set only when that token is passed to the verifyCustomerAccount
mutation with the chosen password, which proves the caller controls the mailbox. This holds even when
requireVerification is false, so a storefront must not assume it can log the customer in straight
after registering. Registering again sends the verification email with a fresh token, for as long as the
credential still holds no password. Once it holds one, registering against the address does nothing, the
same as for any fully registered account.The caller-supplied firstName, lastName, phoneNumber and custom fields are ignored whenever an account
already exists for the address, since the caller has not proven they own it. That includes an account an
administrator created earlier: such a customer registering for themselves keeps the details the administrator
entered. A Customer left by a guest checkout has no account attached, so its details are still filled in.
This is how an existing SSO customer adds a password to their account: call registerCustomerAccount, then verifyCustomerAccount with the emailed token and the chosen password.
requestPasswordReset is the fallback when that token has expired. It works from the moment any registration has touched the account, because the native credential exists from then on, even though it holds no password yet. Completing the reset proves the caller owns the mailbox, so it sets the password and clears the pending verification token in one step. It only does nothing for an account that has never been registered against at all, since there is no native credential to reset.
Without this rule an unauthenticated caller could set a password on someone else's SSO account and then log in as them. See GHSA-wr5h-x3x6-4h23.
A native login on an unverified account is refused for as long as its credential carries a
verificationToken, whatever requireVerification is set to. So if you switch requireVerification from
true to false, customers who registered under the old setting and never verified do not become able to
log in. They finish the flow with the token they were sent, or recover with requestPasswordReset, which
clears the token.
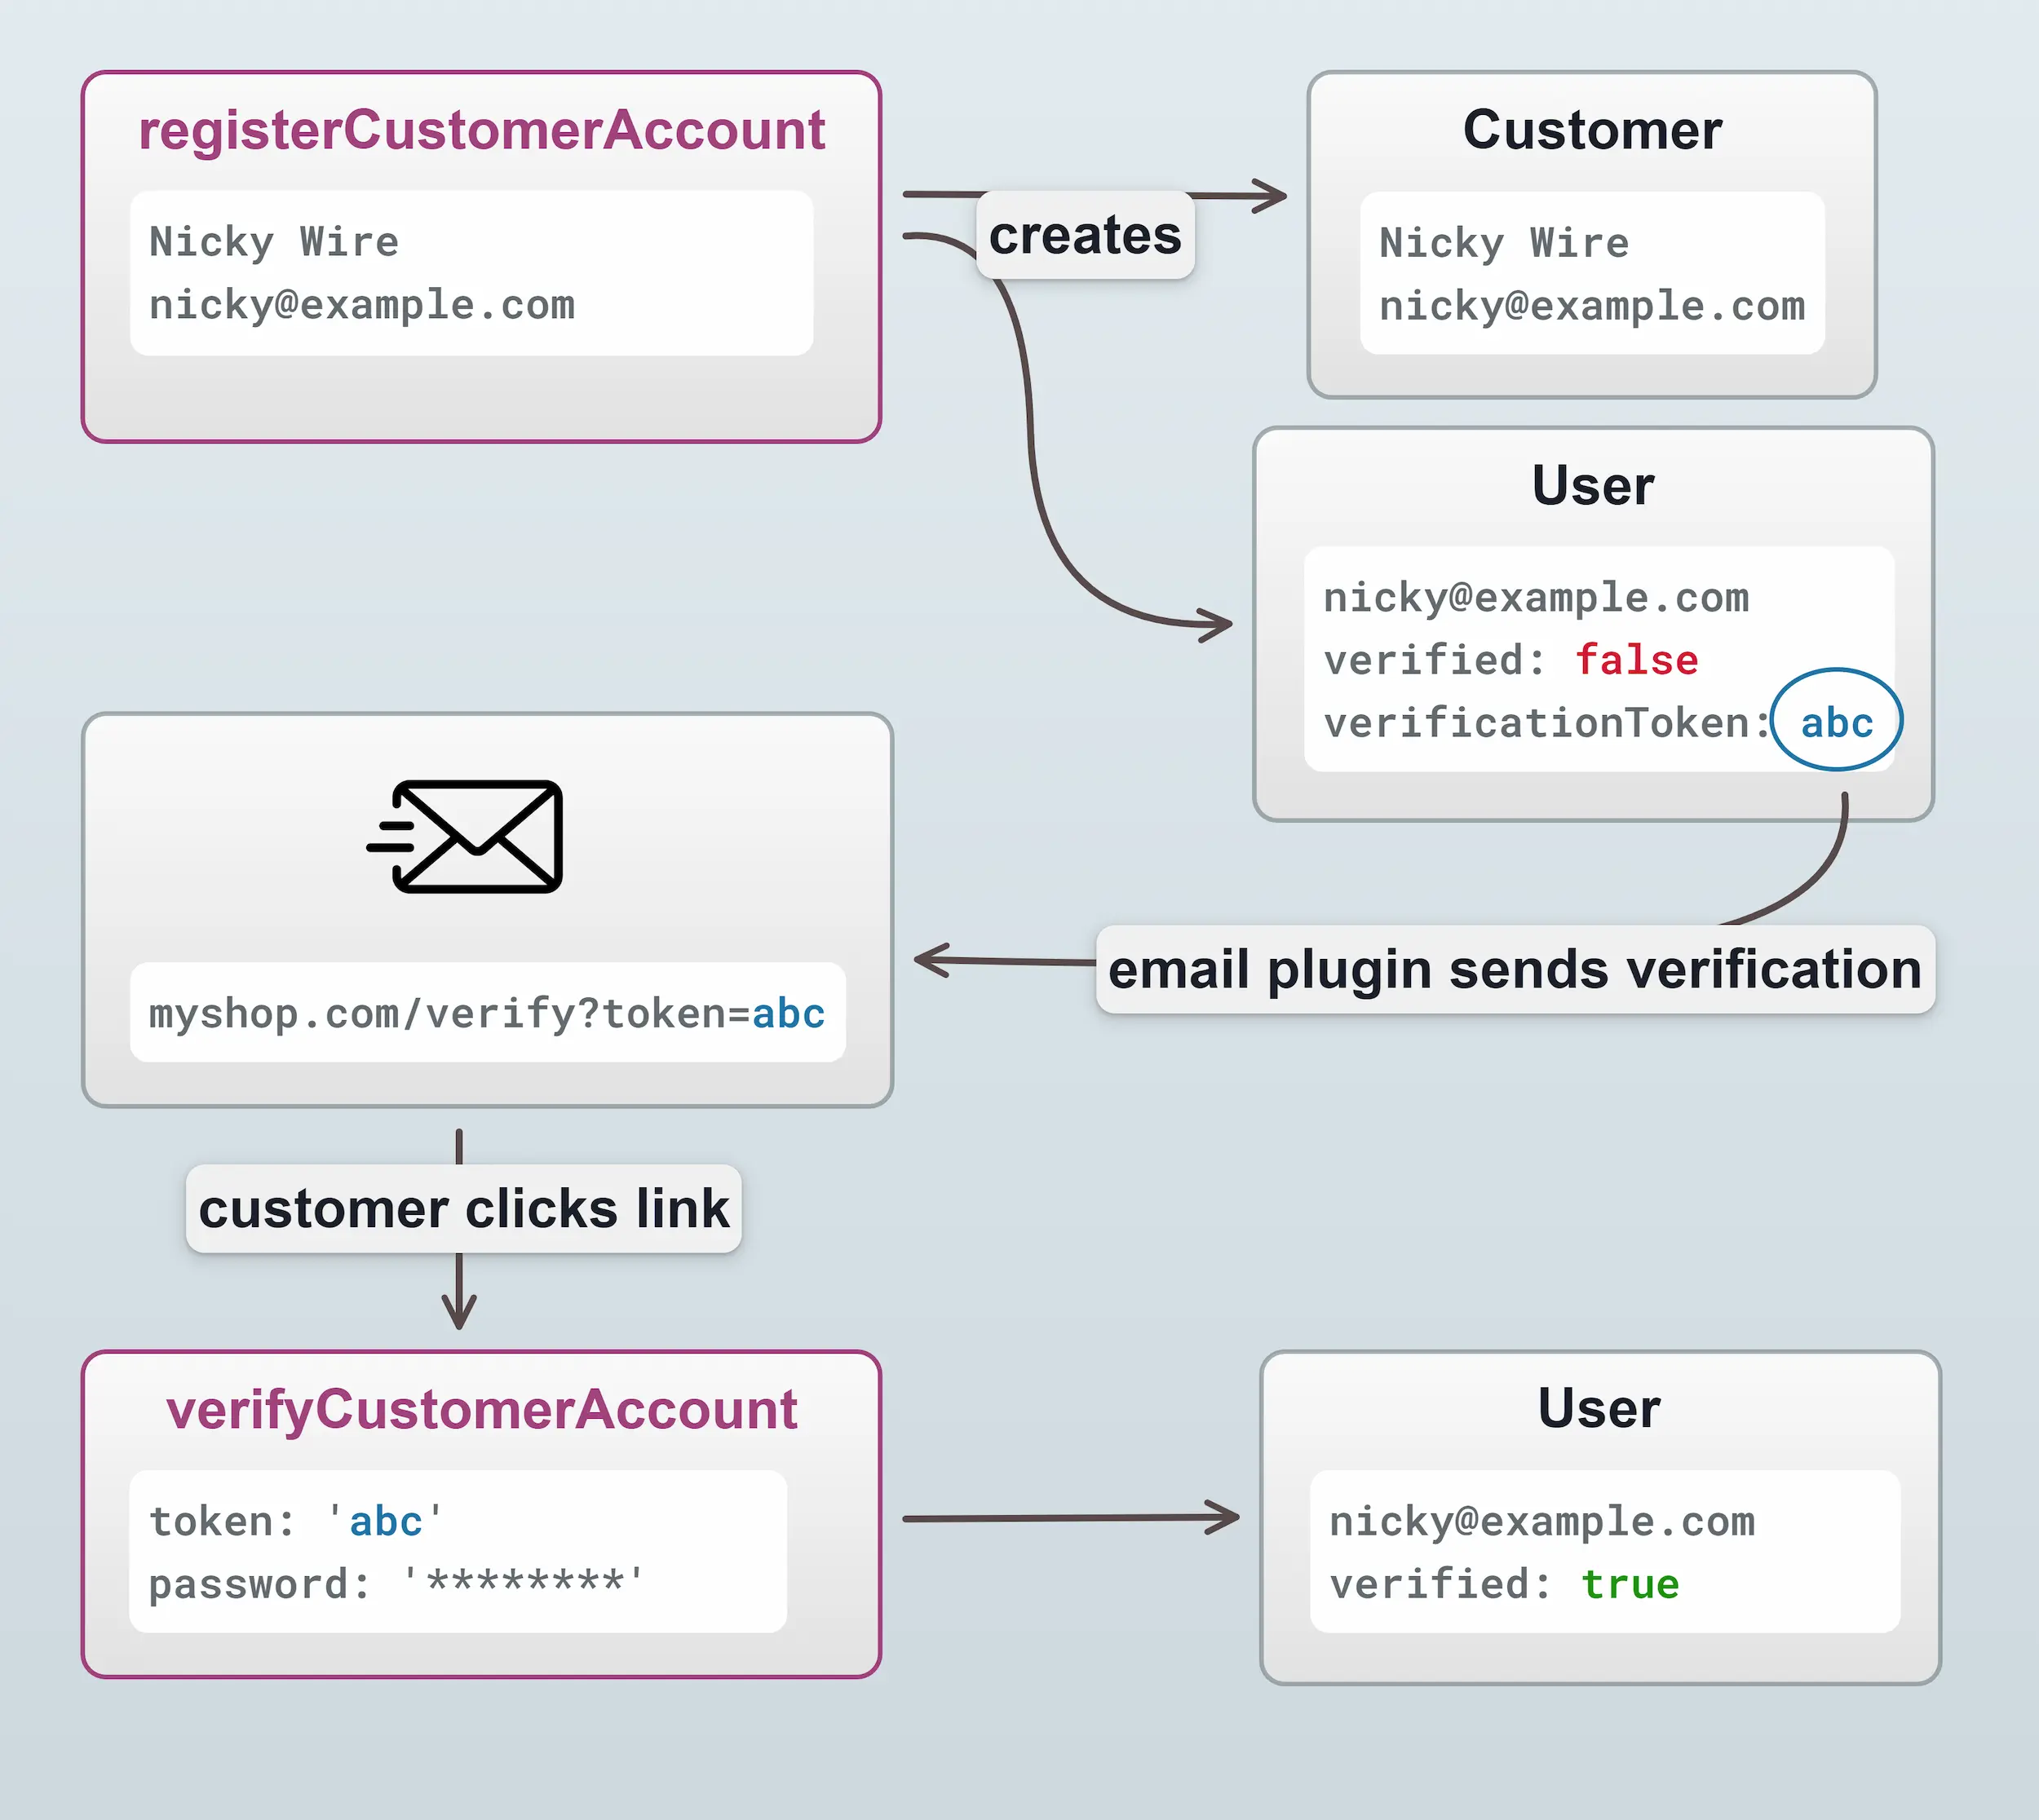
Here's a diagram of the second scenario, where the password is supplied during the verification step.
Here's how the mutations would look for the above flow:
Note that in the variables above, we did not specify a password, as this will be done at the verification step. If a password does get passed at this step, then it won't be needed at the verification step. This is a decision you can make based on the desired user experience of your storefront.
Upon registration, the EmailPlugin will generate an email to the customer containing a link to the verification page. In a default Vendure installation this is set in the vendure config file:
The verification page needs to get the token from the query string, and pass it to the verifyCustomerAccount mutation:
Here's how to implement a password reset flow. It is conceptually very similar to the verification flow described above.
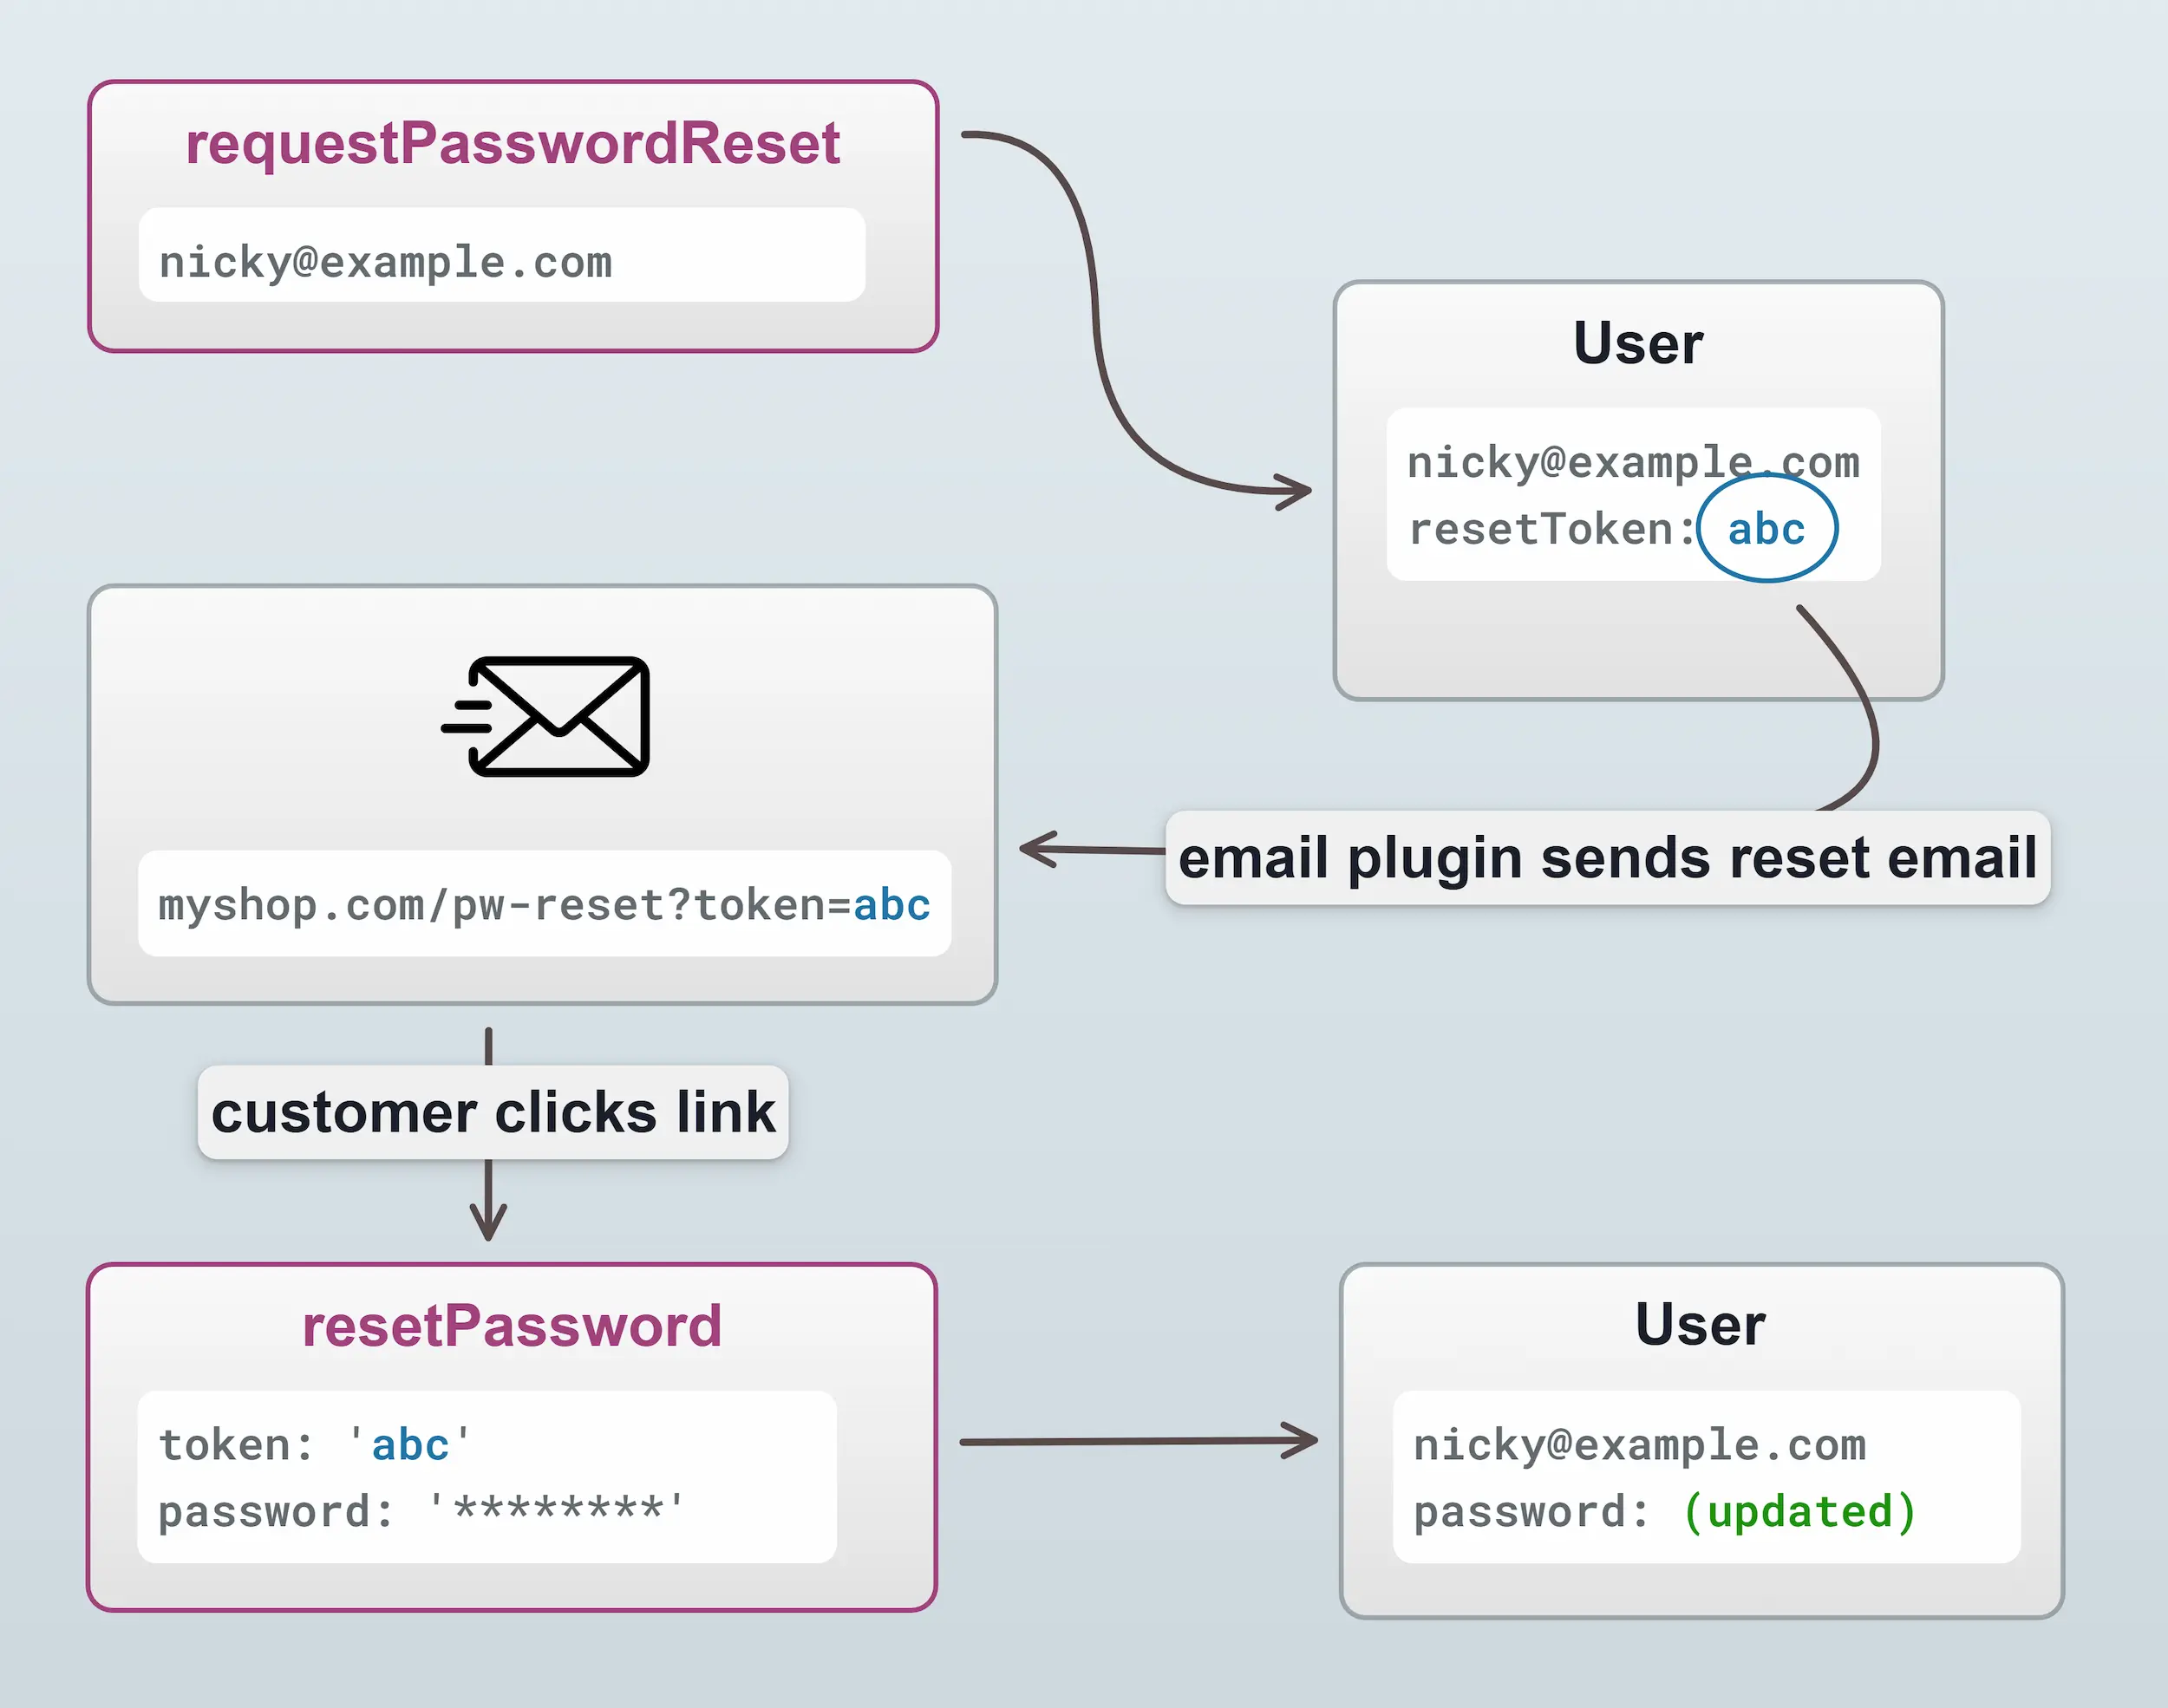
A password reset is triggered by the requestPasswordReset mutation:
Again, this mutation will trigger an event which the EmailPlugin's default email handlers will pick up and send
an email to the customer. The password reset page then needs to get the token from the url and pass it to the
resetPassword mutation:
Architecture reviews, custom plugin work, migrations, ongoing support. Get a hand from the team that builds Vendure.
Talk to the team